
Updated by
Hi, I'm Jack, the owner of Cybersecurity Jobs List and co-founder of Himalayas (himalayas.app) and Cavuno (cavuno.com). Across all my platforms, I work with application security daily: dependency vulnerability scanning, secure authentication, API security, and data protection across hundreds of thousands of users. My technical background is in computer science (UNSW). I studied security engineering and computer networks, and worked as a research assistant on VR experiments that were published in the Journal of Experimental Psychology. I also work with cybersecurity hiring data every day, tracking which companies are posting, what certifications actually appear in listings, how salaries differ by sub-discipline and clearance level, and where the talent gaps are widest. That combination of security practice, engineering at scale, and daily immersion in hiring data shapes the content on this site. I'm currently based in Sydney, Australia.
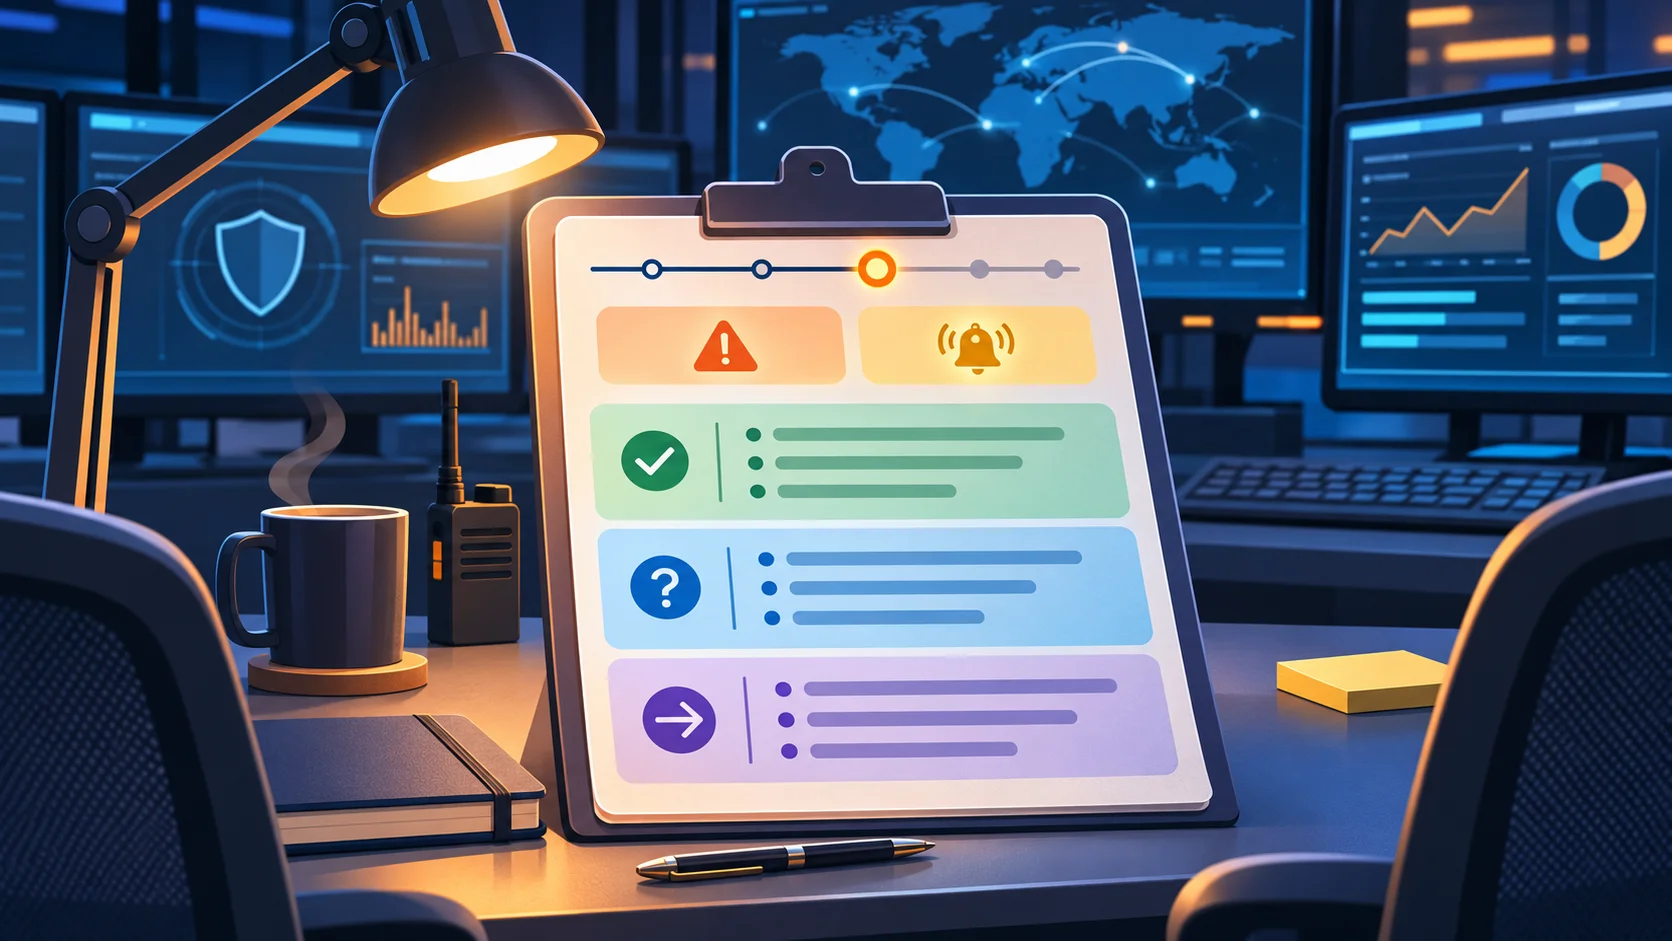
A useful SOC shift handover tells the next analyst what is known, what is still uncertain, who owns the open work, and what to do next. The incoming person should not have to rebuild the case from a wall of chat messages or guess whether an action already happened.
The example and template below use a fictional alert. Adapt the fields to your employer's case system, escalation rules, labels, and access controls. A handover is a work transfer, not a substitute for your organisation's incident plan or later post-incident review.
What belongs in a SOC handover?
Keep the note short enough to scan, but specific enough to continue the work. These six parts usually do that:
- Case and time context: case reference, priority or status under your team's definitions, outgoing and incoming shifts, time zone, and last update.
- Current state: one or two sentences on what triggered the case and where the investigation stands.
- Evidence: what you observed, where it came from, and when it was collected. Link to the approved record instead of copying sensitive data into a second place.
- Actions taken: what changed, who took the action, when, and whether it completed. Separate an action you requested from one that was approved or completed.
- Unknowns and dependencies: what you could not confirm, which data source or person is needed, and any visibility gap.
- Next action and owner: the first concrete task for the next shift, who owns it, and when or under what trigger it needs attention.
Official guidance treats situation reporting and incident logging as distinct but related records. The Australian Cyber Security Centre's practitioner guide provides separate templates for a situation report and an incident log. NIST SP 800-61 Rev. 3 discusses after-action reporting as documentation of the incident, response and recovery actions, and lessons learned. Those are useful references, but your team's procedure decides the format and required fields.
A fictional sign-in alert handover
Imagine an alert for a fictional account, analyst-demo@example.invalid. The identity log shows repeated failed sign-ins followed by one successful sign-in from a new source address. A second authentication log has not loaded, and the approved device inventory has not yet been checked. That is enough to pass on a suspicious sequence. It is not enough to claim the account was compromised or the sign-in was malicious.
| Time (UTC) | Observation or action | Source / result |
|---|---|---|
| 14:03 | Alert received for repeated failed sign-ins | Identity alert `TRAINING-042` |
| 14:08 | One successful sign-in follows the failures | Identity sign-in record; unfamiliar source in this fictional exercise |
| 14:12 | MFA context not confirmed | Authentication log query incomplete; no conclusion recorded |
| 14:20 | Case kept open for review | No account or device action taken in this exercise |
Handover summary: The sign-in pattern is suspicious and remains unconfirmed. The successful sign-in is visible in the identity record, but MFA result, expected user activity, device context, and any resulting session activity are unknown. No containment action was taken. The case remains with the incoming analyst for review under the team's normal priority and escalation rules.
First next action: At the start of the next shift, check whether the missing authentication data is available, then compare the sign-in with approved account and device context. Record the source and time range used. Keep the existing case owner attached until the team process assigns or accepts a new owner. Escalate through the organisation's documented route if its criteria are met. Do not infer approval to disable an account from this note.
This wording gives the next analyst a place to start and a boundary around what the evidence supports. If new data confirms the activity was expected, update the status and explain why. If it reveals an unauthorised session, follow the approved response process and record who authorised each action.
Copyable shift handover template
SHIFT HANDOVER
Date and time written (include time zone):
Outgoing shift / incoming shift:
Author / receiving analyst:
Team-approved priority and status:
Case reference and approved case link:

CURRENT STATE
What triggered the case:
What is known now:
What remains unknown:
Current scope, including any visibility gaps:

EVIDENCE AND TIMELINE
Time (with zone) | Observation or action | Source / record link | Result

ACTIONS TAKEN
Completed actions, actor, time, authority/approval, and result:
Requested or pending actions, approver/owner, and current status:

NEXT ACTION
First task for incoming shift:
Owner:
Due time or trigger:
Escalation route if team criteria are met:

HANDOVER CHECK
Incoming analyst acknowledgement and time:
Questions or missing context:
Next update owner and expected time:
Treat labels such as severity, priority, confirmed, contained, and resolved according to your team's definitions. Include a source link or record identifier that the incoming analyst can access. If a log source is unavailable, say so plainly and name the missing source; a blank field can look like somebody checked and found nothing.
Make the next action easy to pick up
Write in time order and use direct verbs: observed, queried, requested, approved, blocked, or completed. “EDR checked” leaves questions. A useful entry says which approved record or time window was checked and what it showed, without pasting restricted data into the handover.
Keep evidence and interpretation separate. “The record shows a successful sign-in at 14:08 UTC” is an observation. “The attacker logged in” is a conclusion that needs supporting evidence. If you cannot verify something before shift change, name the gap and give it an owner.
One open item should have one next action. “Continue investigating” gives the next shift a queue, not a starting point. “Review the MFA result for the 14:08 sign-in and update the case by 15:00 UTC” is specific. Use your team's own deadlines and escalation thresholds; the example is illustrative, not an operational rule.
Close the loop with the incoming analyst. Ask them to confirm they can open the linked case and understand the first task. A written note plus a brief verbal transfer can expose a missing permission, unclear owner, or time-zone mix-up before the outgoing shift leaves. Google Cloud's SecOps guidance and ServiceNow's handover workflow both emphasize transferring active-case context and tasks between shifts. The exact tool and approval flow vary by team.
How to practise this for a SOC role
You can demonstrate handover writing in a portfolio without using real employer data. Build a small fictional alert sequence from synthetic events, mark every account and record as fictional, and write a handover that identifies the evidence source, unresolved questions, and one next action. Include a short note explaining what evidence would change your assessment.
Do not upload employer tickets, customer data, real indicators, or screenshots from a previous job. Do not present a lab as a real incident. A reviewer should be able to see what you observed, what you inferred, what you could not establish, and how you respected authorization boundaries.
For more context, compare the responsibilities in our SOC analyst versus incident responder guide, then browse current cybersecurity jobs and read each employer's roster, location, and experience requirements. Our guides to cybersecurity interview preparation and take-home assessments cover adjacent steps in the application process.
Final check before you hand over
- Can the next analyst tell what is observed and what is still a hypothesis?
- Does every open case have a current owner and one clear next action?
- Are times labeled with a time zone and linked to a source record?
- Did you name unavailable data, pending approval, and access limits?
- Could the incoming analyst open the linked case and acknowledge the handover?
A good handover gives the next person a reliable starting point. Record what the evidence supports, say where it stops, and make ownership explicit.
Related posts
Practice a first IAM interview with a failed access-removal ticket, a worked solution and clear explanations of the decisions behind it.
Compare three employer-listed product security openings by the work, geography and experience gates that may shape your fit.
Separate false alarms from benign triggers, run a seven-step triage worksheet, and practice with a labeled fictional privileged VPN alert.