Updated by
Hi, I'm Jack, the owner of Cybersecurity Jobs List and co-founder of Himalayas (himalayas.app) and Cavuno (cavuno.com). Across all my platforms, I work with application security daily: dependency vulnerability scanning, secure authentication, API security, and data protection across hundreds of thousands of users. My technical background is in computer science (UNSW). I studied security engineering and computer networks, and worked as a research assistant on VR experiments that were published in the Journal of Experimental Psychology. I also work with cybersecurity hiring data every day, tracking which companies are posting, what certifications actually appear in listings, how salaries differ by sub-discipline and clearance level, and where the talent gaps are widest. That combination of security practice, engineering at scale, and daily immersion in hiring data shapes the content on this site. I'm currently based in Sydney, Australia.
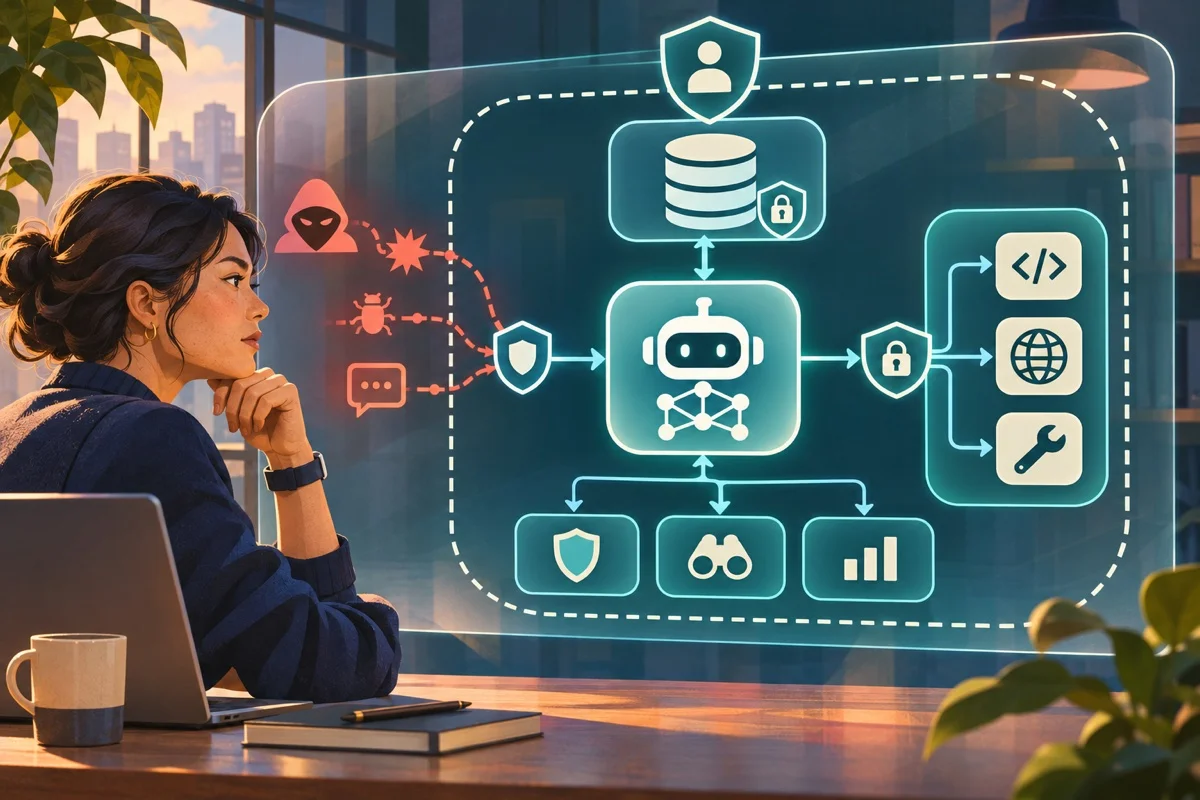
“AI security engineer” can mean very different work from one employer to the next. One team wants a new graduate to build security automation. Another needs someone to put guardrails around internal AI tools. A red team may use AI to improve familiar penetration-testing work.
That difference matters when you decide whether to apply. Here are five employer-listed roles checked on 3 November 2026, with the location and experience details that are easy to miss in a title.
Openings change. The employer page showed each selected listing when checked; check location, eligibility and status again before applying.
Five AI-security roles to compare
| Employer and role | Work that stands out | What the listing asks for | Location or work-mode gate |
|---|---|---|---|
| Brain Co.: AI Security Engineer, 2027 New Grad | Build security tooling and automation for an AI-native product | Designed for candidates finishing a bachelor’s or master’s degree in Spring 2027; prior security experience is not required | San Francisco Bay Area; hybrid |
| Plaid: AI Security Engineer | Review AI systems; build guardrails, identity controls and detection | 3–6 years, plus hands-on experience in at least one listed AI-security area | Seattle, San Francisco or New York offices; hybrid |
| Applied Systems: Security Engineer, AI | Secure LLMs, generative AI and ML infrastructure | 3–5 years in security engineering or DevSecOps is one experience example; foundational ML and security engineering knowledge | US; office or 100% remote according to the posting |
| EY: AI-Native Security Engineer, Senior | Set reusable controls, threat models, tests and response patterns for agentic systems | 5+ years in relevant work, including hands-on ownership of production security controls | Atlanta / “Anywhere in Country” (US); up to 50% travel and hybrid flexibility |
| Hitachi Vantara: Senior Red Team Engineer, Frontier AI Security | Apply frontier AI models to penetration testing, vulnerability discovery and security-tool development | 7+ years in information security, including 4+ focused on penetration testing | Remote California, US; existing US work authorization and no future sponsorship required |
Starting out: Brain Co.’s new-graduate role
This is the clearest early-career opening in this small sample. Brain Co. says prior security experience is not required for its 2027 new-graduate role. It points instead to coursework, CTFs, bug bounties, research or a security-adjacent internship as possible experience. The role is still a full-time engineering job, and its San Francisco Bay Area hybrid location is a real eligibility and commute question, not a minor detail.
If you are still studying, connect your security learning to something you built or tested. Explain what the system was allowed to do, what you tried, what happened and what you changed. Be precise about whether it was a course project, a lab or production work.
Moving from security engineering into AI: Plaid and Applied Systems
Plaid describes work on its own AI systems: pre- and post-deployment reviews, agent guardrails and sandboxes, AI identities, prompt-injection mitigation and security tooling. The listing asks for 3–6 years and hands-on experience in at least one of several relevant AI-security areas. That leaves room for different backgrounds, but it is not the same as saying any security engineer can skip the AI-specific evidence.
Applied Systems frames its role around securing models and the infrastructure around them. The posting names prompt injection, model poisoning, data exposure, AI/ML platforms and pipelines alongside familiar areas such as containers, cloud security, infrastructure as code and software supply chains. Its “3–5 years” wording is one example of experience it seeks, and the page says the person may work from an office or fully remotely within the US.
If your background is AppSec, product security, cloud security or DevSecOps, map your existing work to the system around the model: APIs, identity, secrets, data paths, build pipelines and runtime controls. Then show one careful example of how you tested an AI-specific risk.
Building production controls: EY
EY’s senior role is broader than a sequence of model tests. It describes reusable threat models and control patterns, delivery-pipeline checks, runtime signals, response and work with product and engineering teams. The employer asks for at least five years of relevant experience and hands-on ownership of production security controls. The listing also says up to 50% travel and hybrid flexibility, despite the “Anywhere in Country” location wording.
That makes the role a closer fit for someone who has already turned security findings into controls that teams operate. If you apply, be ready to explain one control from threat to deployment: what risk it addressed, how it was tested, who owned it and how you knew it remained effective.
Using AI in traditional red-team work: Hitachi Vantara
This title includes “Frontier AI Security,” but the posting’s core is senior red-team and penetration-testing work across applications, APIs, networks, cloud and enterprise systems. It asks for seven or more years in information security, including at least four focused on penetration testing. AI appears as a way to improve testing and build tools, rather than a claim that the role is mainly testing AI models.
The location and work authorization rules are narrow: remote California, and candidates must already be authorized to work in the United States without current or future sponsorship. If you are outside that eligibility group, the role is not a remote job you can assume is available worldwide.
A practical way to judge your fit
Use this short worksheet against the employer’s actual requirements:
1. Name the system. What model, application, agent, data source or tool was in scope? Was the work in an authorized lab, a course project or a production environment? 2. Draw the boundary. Show where user input, retrieved content, model output, identities and external tools cross trust boundaries. 3. Choose one risk. For example, could untrusted retrieved text influence a tool call, could a model output reach an unsafe downstream function, or did an agent have more permission than the task needed? OWASP’s prompt-injection guidance explains why retrieval and fine-tuning alone do not eliminate that risk. 4. Test a control, not just a prompt. Record the expected and actual result for safe and adversarial cases. Where an agent can act, document the permission boundary and any separate validation or approval step. OWASP’s AI Agent Security Cheat Sheet is a useful source for least privilege, input validation and testing ideas. 5. Write the result honestly. State what you tested, what failed, what you changed and what remains uncertain. Don’t describe a local demonstration as a production deployment.
This gives you evidence for several kinds of role without pretending all AI-security teams want the same specialty. It also gives an interviewer a concrete starting point for discussing your judgment.
Questions to ask before investing in an application
- Which systems and data would I secure, and which are operated by another team or vendor?
- Is the work mainly application security, agent/tool controls, model evaluation, AI-assisted penetration testing, governance, or a mix?
- What does the engineer personally build, test and operate after a review is complete?
- Which locations, office days, travel expectations and work-authorisation rules apply to this requisition?
- Can I test in a dedicated environment, and how are tool permissions and high-impact actions controlled?
- What evidence would show that the role is succeeding after six months?
A search for “AI security” can return all five kinds of work. Choose the posting that matches the work you want to do and the evidence you can honestly show. Browse cybersecurity jobs on CSJL for adjacent security roles, or use our guides to move from software engineering into application security, prepare for a cybersecurity interview, and turn projects into résumé evidence.
Openings checked 3 November 2026. Employers may close, edit or replace listings at any time. Follow the employer link and confirm eligibility before preparing an application.
Related posts
Clarify scope, timebox a cybersecurity take-home assessment and show your reasoning with a fictional evidence log and copyable report notes.
A worked threat-modeling example for a fictional booking app, with a data-flow map, one authorization risk, a testable requirement, and a portfolio worksheet.
A practical cybersecurity return-to-work guide: map earlier experience to current role tasks, refresh a specific gap, and prepare a clear, honest explanation.